Compliance & Certification
Be ready for the audit before the auditor arrives
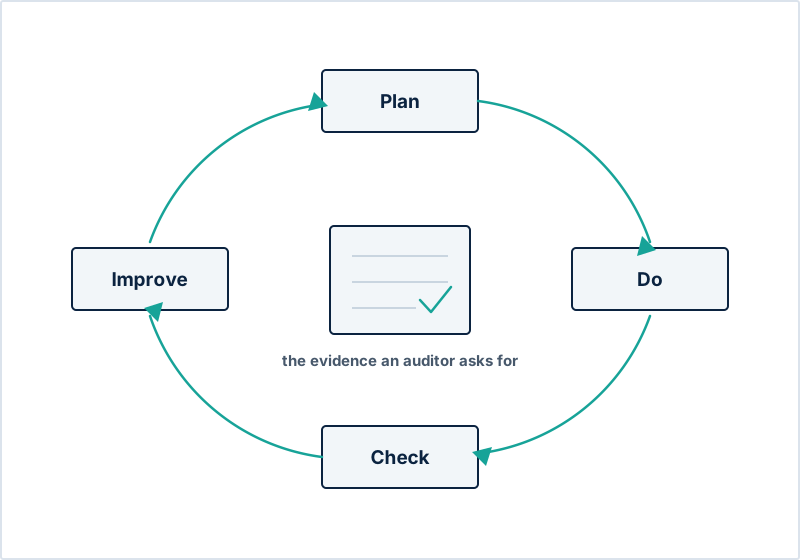
Certification is not a document you buy. It is evidence that your company does what it says it does, gathered over months and tested by an external auditor. We build that evidence with you.
Standards
ISO 27001, 9001, 22301, 20000-1, 27701, 45001, 14001
Typical timeline
Six to twelve months for a first management system
Documentation
Yours, in editable form, at handover
What we do, and what we don’t
We prepare you for certification. The certificate itself is issued by an accredited certification body after a formal audit — we are not that body, and no consultancy is. Anyone who implies they can hand you an ISO certificate is selling you documents that will not survive the audit. What we do is make sure you pass.
Management systems
The standards your clients are asking for
Most companies come to us because a client, a bank or a tender asked for a certificate. We start by telling you whether you actually need it — and if you do, what the real timeline and cost look like before you commit to anything.
- Scope definition and risk assessment
- Statement of applicability and control selection
- Policies and procedures written for your company
- Technical controls implemented by our own engineers
- Internal audit, management review and certification support
Coverage
The frameworks we work to
International standards
- Information and cybersecurity: ISO/IEC 27001, ISO/IEC 27017, ISO/IEC 27018, NIST CSF.
- Cloud: ISO/IEC 27017, ISO/IEC 27018, CSA Cloud Controls Matrix (CCM).
- Business continuity: ISO 22301.
- IT governance and controls: COBIT 2019, ITIL 4.
- Privacy and data protection: ISO/IEC 27701, PCI DSS.
Regional frameworks and regulations
- Jordan — data protection: Personal Data Protection Law No. 24 of 2023.
- Jordan — financial sector: CSF for the Jordan financial sector.
- Saudi financial sector: SAMA CSF, SAMA BCM, SAMA CTI.
- Saudi national cybersecurity: NCA cybersecurity regulations.
- Saudi data governance: NDMO standards and regulations.
- Saudi Aramco: cybersecurity standards.
How an engagement runs
Six stages, priced before you start
You see the cost and the timeline after stage one, not after you have already committed.
Gap assessment
We measure you against the standard as you are today, and give you a written gap report with a realistic cost and timeline.
Design
Scope, risk assessment, statement of applicability, and the control set you actually need.
Implementation
Policies, procedures and technical controls put in place — our engineers do the technical half, not just write about it.
Evidence
Records, logs and management reviews built up so there is something real for the auditor to examine.
Internal audit
We audit you first and fix what we find, while it is still cheap to fix.
Certification support
We prepare you for the external audit and stay with you through it.
Data protection
Jordan’s data protection law, handled properly
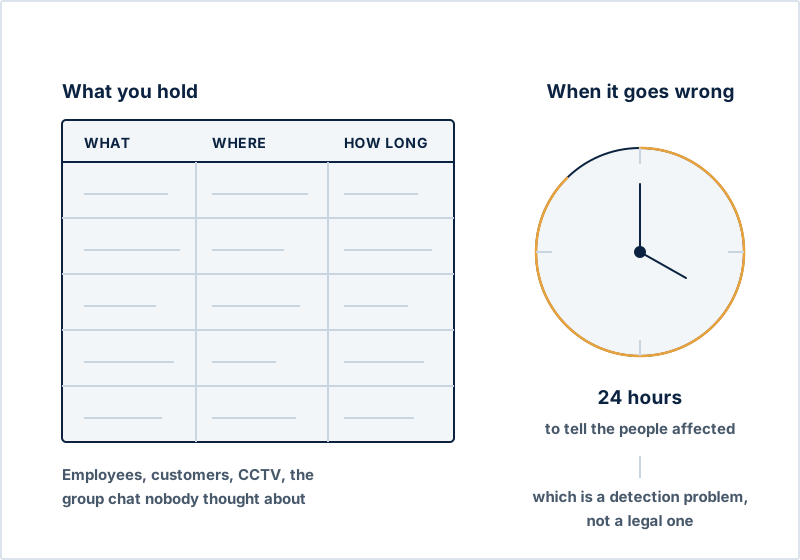
The Personal Data Protection Law No. 24 of 2023 has been fully in force since March 2025. It applies to your customer records, your payroll and your accounting files. Most companies we speak to have not started.
- Gap assessment and compliance roadmap
- Records of processing activities
- Consent mechanisms and privacy notices
- Breach procedures that meet the 24-hour and 72-hour requirements
- Data Protection Officer support, including as an outsourced service
- Cross-border transfer assessments
Policies & internal audit
Findings closed, not filed
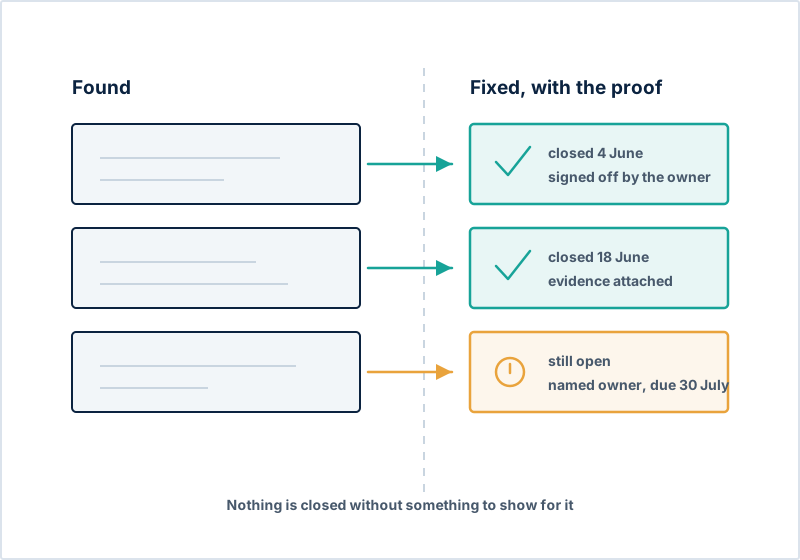
An audit report nobody acts on is worse than no audit — it proves you knew. We audit, then track each finding to closure, so the next external auditor sees a system that corrects itself.
- Security and IT policies written for your company, not copied from a template
- Standard operating procedures your staff can actually follow
- Internal audit programmes and audit execution
- Management review preparation
- Corrective action tracking through to closure
What you actually receive
Documents you own, in editable form
Nothing locked to us. If you change consultant next year, everything we wrote goes with you.
Gap report
Where you stand against the standard, with findings ranked by effort and impact.
Management system
Policies, procedures and records — editable, and written in your company’s language.
Internal audit file
Audit plan, findings, corrective actions and evidence of closure.
Executive summary
Five minutes of reading for the people who sign the budget.
Start with the free gap check
Ninety minutes measuring where you stand against ISO 27001 or Jordan’s data protection law. A written gap summary and a realistic view of the time and cost to close it.
Book a free compliance gap check